
Dark web monitoring isn't about browsing shady websites yourself. Think of it as a specialised intelligence operation, constantly scanning the internet's hidden corners—the illicit forums and marketplaces—for your company's stolen data, like employee emails and passwords.
It’s designed to give you a critical head start. By finding your organisation's compromised credentials before criminals can exploit them, you get the early warning needed to prevent what could otherwise become a devastating attack.
Table of Contents
- What Dark Web Monitoring Means for Your Business
- How We Find Your Compromised Data
- Benefits and Limits of Dark Web Monitoring
- From Alert to Action: Our Response Plan
- Making Monitoring Part of Your Security Strategy
- Your Dark Web Monitoring Implementation Checklist
- Frequently Asked Questions
What Dark Web Monitoring Means for Your Business
Imagine a sprawling, hidden marketplace where your company’s keys—your login details—are being actively traded. Dark web monitoring is like having a dedicated security guard constantly patrolling that marketplace on your behalf. For any UK business, but especially those in tightly regulated sectors like legal, finance, or manufacturing, this is no longer a luxury; it's a critical layer of modern defence.
The goal here is simple: find your exposed credentials before a digital burglar can use them to unlock your systems. This flips your security posture on its head. Instead of reacting to a breach and cleaning up the mess, you're proactively identifying and neutralising threats before they ever hit your network.
To give you a clearer picture, here’s a quick summary of what this service delivers.
Dark Web Monitoring at a Glance
| Aspect | Description for Your Business |
|---|---|
| Core Function | Continuously scans hidden online marketplaces for your stolen data. |
| Key Benefit | Provides early warnings about compromised employee credentials. |
| Outcome | Allows you to secure accounts before a cyberattack occurs. |
| Business Impact | Prevents financial loss, reputational damage, and operational downtime. |
| Best For | All businesses, but essential for those in legal, finance, and manufacturing. |
In short, it’s about turning the tables on attackers by using their own hunting grounds against them.
The Staggering Scale of the Credential Threat
It's hard to overstate the size of this problem. Right now, there are over 15 billion stolen account credentials circulating on dark web marketplaces. It’s a grim reality, but organisations whose details appear on the dark web face a 2.56x higher risk of suffering a cyberattack.
And with around 80% of all email data having been leaked at some point, the odds are high that some of your company's information is already out there.

From Intelligence to Action
Simply finding exposed data isn't enough. The real power of dark web monitoring comes from the actionable intelligence it provides. When the service finds your information, it triggers an immediate, targeted response.
Key Takeaway: Dark web monitoring transforms abstract threats into specific, actionable alerts. It tells you which employee account is compromised, where it was exposed, and when, allowing you to take immediate, targeted action.
What does this look like in practice?
- Early Detection: The system flags credentials that have been leaked, often from breaches at third-party services your employees use with their work email.
- Risk Assessment: You can instantly gauge the severity. Is it a single junior employee's login, or does it belong to a senior executive with privileged access?
- Guided Remediation: The alert gives you the precise information needed to act, such as forcing a password reset and enabling multi-factor authentication on the affected account.
This early warning is fundamental to protecting everything from your financial accounts to your sensitive intellectual property. It's a cornerstone of a robust security strategy, a topic we cover in more depth in our small business cyber security guide. By actively searching for these hidden threats, you can ensure your defences are ready for whatever comes next.
How We Find Your Compromised Data
To protect your organisation, you first need to know where attackers are hiding and what information they have. Our dark web monitoring service is essentially your intelligence unit, but it’s crucial to understand we’re not browsing dangerous sites or forums. Think of it less like surfing the web and more like running a highly targeted search across vast, private databases of stolen information.
We’ve built up access to huge, indexed collections of leaked data gathered from thousands of breach sources. This approach is safe, legal, and focused purely on intelligence. It’s all about finding threats before they find you.
Our Combination of Technology and Expertise
So, how do we actually do it? Effective dark web monitoring isn’t just about having the right software; it's a blend of powerful automation and real human insight. We combine advanced, AI-driven scanners with the experience of our security analysts to make sure nothing gets missed.
AI-Powered Scanners: These tools are our frontline observers, working 24/7. They constantly scan known breach repositories, criminal marketplaces, and logs from information-stealing malware. They can sift through billions of records in a flash, flagging any data that might be linked to your company.
Human Intelligence Analysts: But technology alone can’t see the whole picture. Our security experts step in to verify everything the scanners find. They filter out the noise and false alarms, adding the kind of critical context only a person can provide. They know the subtle signs of an emerging threat on a forum that an automated tool might completely overlook.
This two-pronged approach gives us the sheer scale of machine-driven discovery and the sharp precision of human verification. It ensures the alerts you receive are real, relevant, and actionable.
What We Look For
Our search is laser-focused. We aren't just looking for random bits of data; we’re hunting for the specific assets that cybercriminals use to break into a business like yours.
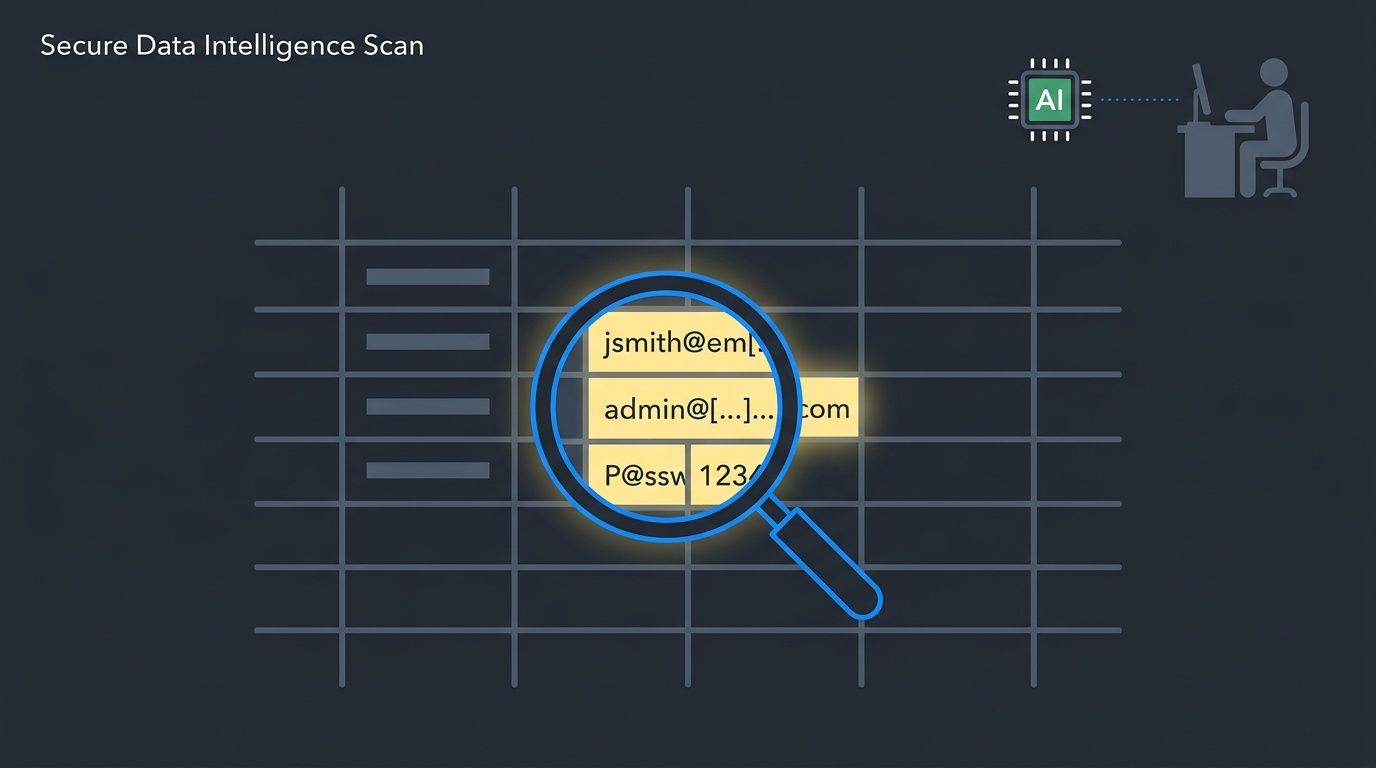
The main targets include:
- Employee Credentials: Work emails paired with passwords from other website breaches are gold dust for attackers. It’s the most common way they get their foot in the door.
- Corporate Logins: We search for credentials that give direct access to your business systems, cloud accounts, and other critical platforms.
- Sensitive Company Files: Our monitoring can also spot if your intellectual property, financial records, or strategic plans have been stolen and are being sold.
- Client Information: Finding your clients' data on the dark web can be devastating for your reputation and lead to serious legal trouble.
Discovering compromised data is the first step in a proactive security plan. This intelligence allows you to act decisively, a concept that is a core part of effective data leak prevention for any organisation. By knowing exactly what has been exposed, you can take precise steps to close security gaps before they are exploited.
This early warning gives you the power to act fast. To get a better sense of the risk, read our article explaining how criminals can access your accounts without your password. Ultimately, it’s this early detection that turns a potential disaster into a manageable security task.
Benefits and Limits of Dark Web Monitoring
So, what does dark web monitoring actually do for your business? For firms in sectors like legal, finance, and manufacturing, the benefits are immediate and very real. It’s one of the most effective ways to get ahead of security threats and prove to clients and regulators that you're taking cybersecurity seriously.
The biggest win here is preventing account takeovers. Imagine finding out that the login details for a senior partner at your law firm, or an engineer with access to all your sensitive designs, have been leaked. Dark web monitoring gives you that information, often within hours of it appearing for sale, letting you stop a devastating breach before it ever happens. This isn't just about protecting your intellectual property and client data; it’s also a clear signal to auditors that you’re meeting your compliance duties under frameworks like GDPR and Cyber Essentials.
Real-World Gains for Your Business
By bringing a dark web monitoring service on board, you’re not just buying a piece of tech; you're gaining a crucial advantage. Here’s what that looks like day-to-day:
- Spotting Threats Early: You get an alert the moment an employee’s credentials pop up in a data breach or on a criminal forum. This gives you a critical head start to respond.
- Guarding Your Intellectual Property: You can stop attackers before they use stolen logins to walk away with priceless design files, financial projections, or trade secrets.
- Strengthening Your Compliance Position: It's concrete proof to regulators, insurers, and clients that you have robust systems in place to find and deal with emerging cyber threats.
- Cutting Down Business Risk: When you proactively shut down compromised accounts, you massively reduce your chances of falling victim to a ransomware attack or a major data breach.
Understanding the Limitations
It's just as important, however, to be clear-eyed about what dark web monitoring isn't. A realistic understanding helps you build a genuinely strong security strategy and sets proper expectations.
Key Insight: Dark web monitoring is a detective control, not a preventative one. Think of it as a top-of-the-line burglar alarm. It tells you instantly that a window has been smashed, but it can’t stop a brick from being thrown in the first place.
This distinction is absolutely vital. The service can't stop one of your team's passwords from being scooped up in a breach on a third-party website they use. Its job is to make sure you know about that breach immediately so you can slam the door shut before any damage is done.
That's precisely why it can't work in a silo. Relying only on monitoring is like having that expensive alarm system but never bothering to lock your doors. The intelligence it provides is most powerful when it’s connected to your other security layers. An alert for a compromised password should automatically trigger a forced reset and could be the perfect reason to finally enforce Multi-Factor Authentication (MFA) on that account.
Ultimately, dark web monitoring is an essential part of modern, layered defence. It provides the critical, real-time intelligence you need to make all your other security tools work that much harder.
From Alert to Action: Our Response Plan
Finding your company’s data on the dark web is a gut-wrenching moment. But a discovery is useless without a plan. The real measure of a dark web monitoring service isn’t just finding the threat; it’s about what happens in the minutes and hours that follow.
A structured response plan is what turns a worrying piece of data into actionable intelligence. It's the difference between panic and a calm, methodical process to neutralise the threat before it can cause real damage.
At Blowfish, we’ve built our entire response around this idea. We don't just send you an automated alert and leave you to figure it out. We're with you every step of the way, providing expert guidance from the initial flag right through to a successful resolution.
Our five-stage process, shown below, gives you a clear picture of what to expect when our systems find something that needs your attention.
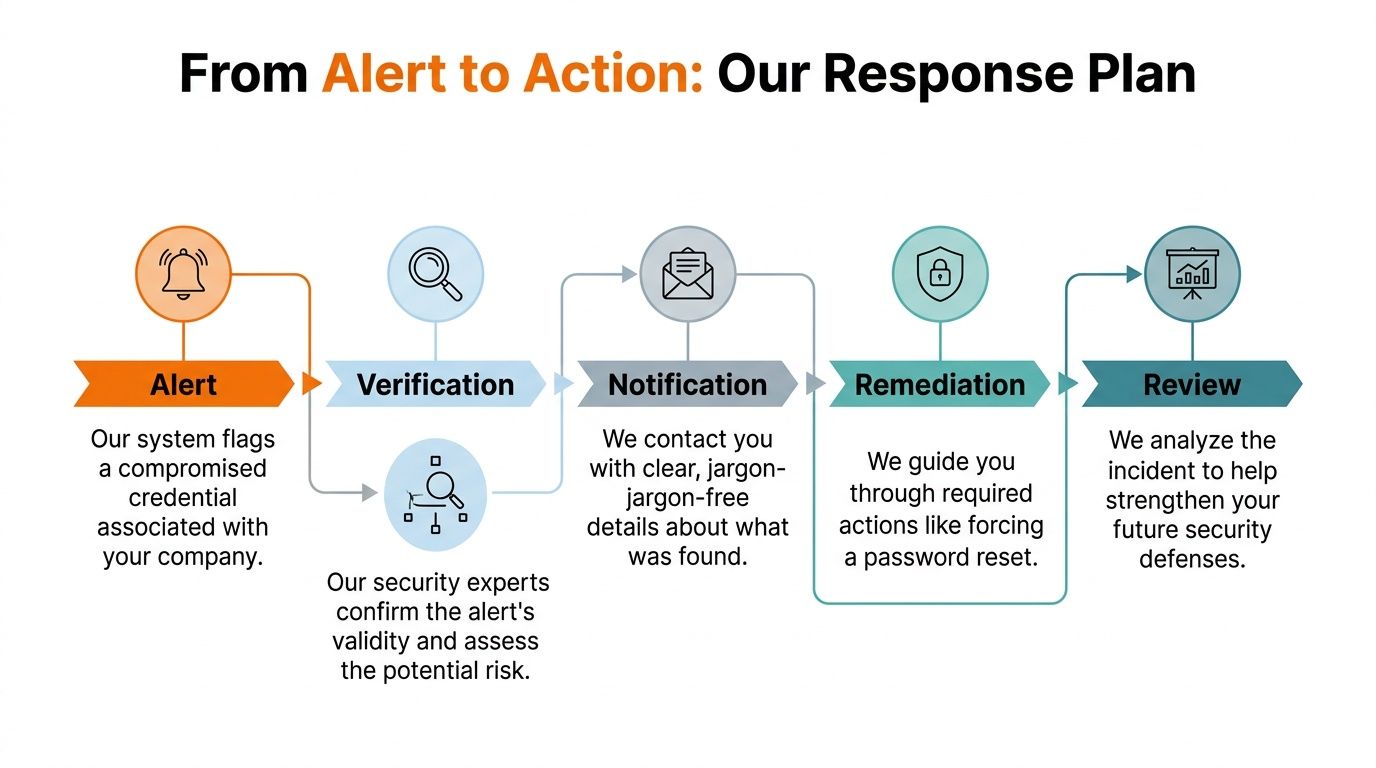
This workflow ensures every alert is handled with the urgency and expertise it deserves, turning a potential crisis into an opportunity to strengthen your defences.
Our Incident Response Workflow in Detail
So, what happens when one of our probes gets a hit on a credential linked to your business? Our response plan kicks in immediately. We’ve refined this process over years of experience to be as efficient and low-stress for you as possible.
The table below breaks down exactly how we move from a raw alert to a fully resolved incident, showing the actions we take and how they directly benefit your organisation.
Incident Response Workflow
| Step | Action Taken by Blowfish | Benefit to Your Business |
|---|---|---|
| 1. Alert & Verification | Our systems generate an instant alert. Our security analysts immediately verify its authenticity, checking it against known breaches and assessing the risk level. | You're not bombarded with false positives. We filter out the noise, so you only focus on genuine, prioritised threats. |
| 2. Context & Analysis | We investigate the source of the leak and determine the potential impact. Is it a single user password or an administrative account? What other data was exposed alongside it? | You get the full picture, not just a single data point. This context is crucial for understanding the true scope of the risk. |
| 3. Notification & Guidance | We contact your designated point-of-contact with a clear, jargon-free report. We explain what was found, what it means, and provide straightforward remediation steps. | You receive actionable advice you can follow immediately. There’s no panic, just a clear set of instructions to contain the threat. |
| 4. Containment & Remediation | We guide your team through the necessary actions, like forcing a password reset for the affected user, checking for suspicious activity, and ensuring multi-factor authentication (MFA) is active. | The immediate danger is neutralised quickly and effectively, minimising the window of opportunity for an attacker. |
| 5. Review & Strengthen | Once contained, we work with you to understand the root cause. Was this a one-off mistake, or does it highlight a need for staff training or a policy review? | You turn a reactive incident into a proactive security improvement, strengthening your overall posture to prevent future breaches. |
This structured approach means that even when facing a confirmed threat, you have a clear path forward.
Our promise is simple: you’re never on your own. A managed service means having a dedicated security partner in your corner, ready to provide the expertise and support needed to handle any threat swiftly and effectively.
By turning incidents into learning opportunities, we don't just fix the immediate problem. We help you build a more resilient and secure organisation for the long term.
Making Monitoring Part of Your Security Strategy
Real cybersecurity isn't about buying a single piece of software; it's about building layers of defence that all talk to each other. Think of dark web monitoring not as a standalone tool, but as the lookout in your castle's watchtower. It spots threats from a distance and alerts the guards, giving them the crucial head start they need to react.
The intel you get from scanning criminal forums and marketplaces provides the 'why' behind your security actions. It turns a collection of separate tools into a smart, coordinated defence system. This is where you see the real value, as each part of your security setup starts making the others more effective.
How Intelligence Amplifies Your Defences
An alert from a dark web monitoring service is far more than a simple notification. It’s the starting gun that kicks off a chain of protective actions across your entire security infrastructure, allowing you to act with surgical precision instead of just guessing where the danger might be.
Let’s walk through a common, real-world scenario. Our system flags an employee's password after it shows up in a new data breach being sold online. That single piece of information immediately puts other defences on high alert:
Endpoint Detection and Response (EDR): The EDR software protecting that employee’s laptop can be put into a heightened state of alert. We know that account is now a prime target, so any activity from that device will be scrutinised far more closely.
Identity Threat Detection and Response (ITDR): Your ITDR platform takes this alert as critical context. If it then sees an unusual login attempt for that user—even with the correct (but stolen) password—it can instantly flag the activity as high-risk and block it.
Multi-Factor Authentication (MFA): The alert gives you a clear, evidence-based reason to tighten MFA policies. You can force the user to re-authenticate immediately and confirm that MFA is permanently switched on for their account.
Strengthening Password Security
This kind of intelligence also works hand-in-glove with tools like password managers. Many people think a long, complicated password is all they need to be safe. But dark web monitoring shows you exactly when that "strong" password has been exposed in a breach on a completely separate website the user signed up for. To properly integrate this, it's worth exploring the best dark web monitoring services to see which solution fits your business.
When your security tools work in concert, your defence is far greater than the sum of its parts. An alert for a stolen password doesn't just prompt a reset; it triggers a system-wide response that hardens your entire security posture against that specific threat.
This integrated approach is the key to building a truly resilient business. You don't just change the compromised password; you use that knowledge to reinforce every related defence. If you want to go deeper on this, we cover more in our dedicated article on robust password management. By connecting detection directly to your response, you create a powerful feedback loop that constantly strengthens your security.
Your Dark Web Monitoring Implementation Checklist
Deciding to start monitoring the dark web is a smart, proactive step. But to get the most out of it, a bit of groundwork is essential. Think of it less like flipping a switch and more like laying the foundation for a much stronger security posture.
This simple checklist will walk you through the key actions to take, ensuring that when the service goes live, it's already focused on what matters most to your business.

Getting Your House in Order First
Before we dive in, let’s get everything aligned. Working through these steps helps us zero in on your unique risks and makes sure your team is ready to respond when an alert comes through.
1. Pinpoint Your Critical Digital Assets
First things first: what are your crown jewels? We need a clear list of the digital assets that absolutely must be protected. This includes all your company domains, key brand or product names, and, crucially, the names of your senior executives or anyone with high-level system access. This list becomes the core of our search.
2. Review and Reinforce Your Internal Policies
A strong password policy is your first line of defence. This is the perfect time to review it and, if needed, tighten it up. Enforcing more complex passwords and a sensible rotation schedule makes a huge difference. If you really want to lock things down, it’s worth looking into how to add two-factor authentication.
3. Get Your Team On Board
Let your employees know that this new security measure is being put in place. It’s important to frame it as what it is: a tool to protect both the company's data and their own personal information that may be tied to their work accounts. Good communication means that when an alert requires action—like an urgent password reset—everyone understands why and is ready to act fast.
A successful dark web monitoring programme isn't just about the tech. It’s about knowing what you need to protect and preparing your people to be part of the solution. Getting these fundamentals right is the key to building a genuinely resilient security culture.
It’s also worth remembering that this type of monitoring works best as part of a wider strategy. Layering your defences with tools from leading cybersecurity platforms like Crowdstrike can dramatically improve your ability to detect and respond to threats across your entire organisation.
With this prep work done, you're in a great position to move forward. The next logical step is to see what your current exposure looks like. Contact our experts today to request a complimentary dark web scan or to schedule a consultation.
Frequently Asked Questions
When we talk to business leaders about dark web monitoring, a few key questions always come up. It's a complex topic, so let's tackle some of the most common ones head-on.
Is Dark Web Monitoring Legal in the UK?
Absolutely. Not only is professional dark web monitoring completely legal, but it’s also now considered a core part of good cybersecurity practice for UK businesses. Think of it as a form of security intelligence, not as browsing criminal forums.
Reputable services don't go poking around illegal sites. Instead, we use safe, specialised tools to scan for data that has already been stolen and dumped onto the dark web. The whole point is detection and defence, not getting involved in anything shady.
How Quickly Will We Know if Our Data Is Found?
Our alerts are practically instant. The moment our systems find a match for your company’s information—be it an email address or a password—the response process kicks off.
Our security team then immediately gets to work verifying the alert to make sure it's genuine and not a false positive. Once confirmed, we notify you directly based on our agreed incident response plan, which usually means you'll hear from us within hours of the initial discovery.
This rapid, verified notification is what makes all the difference. It shrinks the window of opportunity for an attacker to use that stolen data, giving you precious time to act and secure your accounts.
Can Dark Web Monitoring Prevent a Data Breach?
This is a really important distinction to make. Monitoring is a detection tool, not a prevention tool. It can't stop a supplier from being breached or prevent an employee from falling for a clever phishing email.
What it can do is provide a critical early warning. This warning is what stops a minor incident from snowballing into a catastrophic breach of your own network. By finding out a password has been compromised, you can reset it immediately and lock the account. You're essentially stopping the criminal from using a stolen key to open your digital front door.
Ready to see what your company's exposure on the dark web looks like? Contact Blowfish Technology today to request a complimentary scan and start building a more resilient security strategy. Find out more by visiting our website: https://blowfishtechnology.com.

The Blowfish Technology team. Managed IT, cloud services, software development and connectivity for North West businesses since 1999.