
The convergence of information and communications technology has fundamentally transformed how businesses operate, creating unprecedented opportunities alongside equally significant security challenges. ICT cyber security represents the comprehensive approach organisations must adopt to protect their interconnected systems, data, and communications infrastructure from an ever-evolving threat landscape. For UK businesses in 2026, understanding the relationship between information technology and cyber security is no longer optional-it's a fundamental requirement for operational continuity and regulatory compliance.
Understanding ICT Cyber Security Fundamentals
Information and communications technology encompasses the entire spectrum of systems that businesses rely upon daily, from traditional computing infrastructure to telecommunications networks, cloud platforms, and mobile devices. When we discuss ict cyber security, we're addressing the protection of this entire ecosystem against unauthorised access, data breaches, service disruptions, and malicious attacks.
The scope of ict cyber security extends far beyond installing antivirus software or configuring firewalls. It requires a holistic understanding of how information flows through an organisation, where vulnerabilities exist, and which assets require the most stringent protection. Modern ict cyber security frameworks integrate technical controls, policy development, staff training, and incident response planning into a cohesive defence strategy.
The Three Pillars of ICT Security
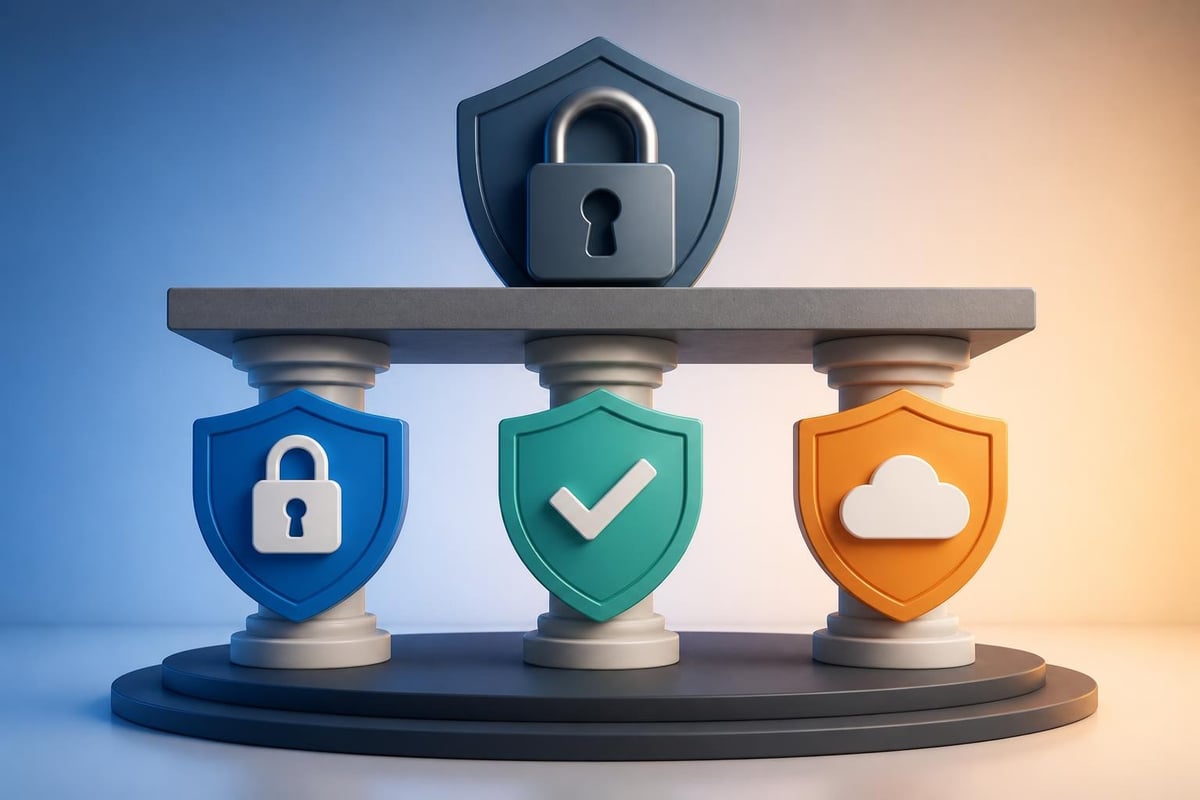
Every effective ict cyber security programme rests upon three fundamental principles that guide protection efforts:
- Confidentiality: Ensuring that sensitive information remains accessible only to authorised individuals and systems
- Integrity: Maintaining the accuracy and completeness of data throughout its lifecycle
- Availability: Guaranteeing that systems and information remain accessible when needed by legitimate users
These principles inform every decision within an ict cyber security strategy, from access control implementation to disaster recovery planning. Organisations that neglect any single pillar create exploitable weaknesses that adversaries can leverage.
Current Threat Landscape Facing UK Businesses
The threat environment confronting organisations in 2026 has grown substantially more sophisticated than even five years ago. Cybercriminals have industrialised their operations, employing business models that rival legitimate enterprises in their sophistication and reach. Understanding these threats is essential for developing proportionate ict cyber security responses.
Ransomware and Extortion Attacks
Ransomware continues to dominate the threat landscape, with attackers increasingly targeting small and medium-sized enterprises that may lack robust defences. Modern ransomware variants employ double-extortion techniques, encrypting data whilst simultaneously threatening to publish sensitive information publicly. The financial and reputational damage can be catastrophic, particularly for organisations without comprehensive backup and recovery solutions.
Supply Chain Vulnerabilities
Sophisticated threat actors increasingly target the weakest links in organisational supply chains rather than attacking well-defended primary targets directly. These supply chain compromises can affect hundreds or thousands of downstream organisations simultaneously, making vendor security assessment a critical component of ict cyber security programmes.
| Threat Type | Primary Target | Business Impact | Mitigation Priority |
|---|---|---|---|
| Ransomware | SMEs, Healthcare | High – Operational disruption | Critical |
| Phishing | All sectors | Medium – Data compromise | High |
| Supply Chain | Manufacturing, Retail | High – Widespread breach | High |
| Insider Threats | Finance, Technology | Medium – Data exfiltration | Medium |
| DDoS Attacks | Online services | Medium – Service disruption | Medium |
The National Cyber Security Centre regularly publishes threat assessments that UK organisations should incorporate into their risk management processes.
Developing an ICT Cyber Security Framework
Building a comprehensive ict cyber security framework requires methodical planning and stakeholder engagement across the organisation. Rather than implementing controls in isolation, effective frameworks align security measures with business objectives and risk tolerance.
Risk Assessment and Asset Classification
Begin by cataloguing all information and communications technology assets within your organisation. This inventory should include hardware, software, data repositories, network infrastructure, and third-party services. Each asset requires classification based on its criticality to business operations and the sensitivity of information it processes or stores.
Risk assessment methodologies help organisations understand which threats pose the greatest danger to specific assets. By evaluating both the likelihood of various attack scenarios and their potential impact, businesses can prioritise security investments where they'll deliver the greatest risk reduction. The Cyber Security Body of Knowledge provides excellent frameworks for structured risk assessment approaches.
Policy Development and Governance
Effective ict cyber security relies upon clear policies that define acceptable use, access controls, data handling procedures, and incident response protocols. These policies must align with regulatory requirements including GDPR, industry-specific regulations, and contractual obligations such as Cyber Essentials certification.
Governance structures should establish clear accountability for security decisions, with executive leadership demonstrating visible commitment to ict cyber security priorities. Regular reporting mechanisms ensure that boards and senior management maintain awareness of the organisation's security posture and emerging threats.
Technical Controls for ICT Infrastructure Protection
Whilst policy and governance provide the foundation for ict cyber security, technical controls implement the actual protective mechanisms that defend against attacks. These controls span multiple layers of the technology stack, creating defence-in-depth that prevents single points of failure.
Network Security Architecture
Modern network security employs segmentation to contain potential breaches and limit lateral movement by attackers. By dividing networks into zones based on trust levels and function, organisations can enforce stricter controls on traffic flowing between segments. Next-generation firewalls, intrusion detection systems, and network access control solutions form the backbone of network-based defences.
For organisations with distributed operations, secure connectivity solutions such as business broadband and leased lines require careful configuration to maintain security whilst supporting remote access requirements.
Endpoint Protection and Management
Every device connecting to organisational systems represents a potential entry point for attackers. Comprehensive endpoint protection extends beyond traditional antivirus to include:
- Advanced threat detection using behavioural analysis and machine learning
- Application whitelisting to prevent unauthorised software execution
- Patch management ensuring timely security updates across all devices
- Device encryption protecting data on lost or stolen equipment
- Mobile device management for smartphones and tablets
The research on explainable artificial intelligence in cyber security highlights how transparent AI models can improve threat detection accuracy whilst maintaining administrator trust in automated systems.
Cloud Security Considerations
As organisations increasingly adopt cloud services, ict cyber security must extend to these environments. Cloud security requires understanding the shared responsibility model-where cloud providers secure the infrastructure whilst customers secure their data, applications, and access controls.
Key considerations include identity and access management, data encryption both in transit and at rest, cloud workload protection, and configuration management to prevent misconfigurations that expose resources publicly. Organisations planning cloud migration strategies must integrate security requirements from the earliest planning stages.
Human Factors in ICT Cyber Security
Technology alone cannot deliver comprehensive security. Human behaviour remains both the greatest vulnerability and the most powerful defence within any ict cyber security programme. Organisations must invest in building a security-aware culture where staff understand their role in protecting information assets.
Security Awareness Training
Regular, engaging security awareness training helps staff recognise common attack techniques such as phishing, social engineering, and pretexting. Training should be relevant to employees' specific roles and responsibilities, using realistic scenarios that reflect the actual threats facing the organisation.
Effective training programmes include:
- Initial onboarding security briefings for all new employees
- Regular refresher sessions covering emerging threats and attack techniques
- Simulated phishing exercises testing and reinforcing training concepts
- Role-specific training for staff handling sensitive information
- Executive briefings ensuring leadership understands strategic security risks
Cultivating Security Champions
Identifying and empowering security champions throughout the organisation creates a distributed network of advocates who promote secure practices within their departments. These champions serve as first points of contact for security questions, helping bridge the gap between technical security teams and operational staff.
Incident Response and Business Continuity
Despite best efforts, organisations must accept that perfect security remains unattainable. Robust incident response capabilities minimise damage when breaches occur, whilst business continuity planning ensures operations can continue or resume quickly following disruptions.
Incident Response Planning
Comprehensive incident response plans define clear procedures for detecting, containing, investigating, and recovering from security incidents. These plans should designate specific roles and responsibilities, establish communication protocols, and provide decision-making frameworks that function even under the stress of active incidents.
Testing through tabletop exercises and simulated attacks validates that response procedures work as intended and that staff understand their responsibilities. The NIST guide to cyber threat information sharing provides valuable frameworks for coordinating responses across organisational boundaries.
| Response Phase | Key Activities | Responsible Parties | Success Criteria |
|---|---|---|---|
| Detection | Monitoring, alerting, triage | SOC team, automated systems | Incident identified within 1 hour |
| Containment | Isolation, access revocation | Security team, IT operations | Threat spread prevented |
| Investigation | Forensics, root cause analysis | Security specialists | Attack vector identified |
| Remediation | System restoration, patching | IT operations, vendors | Vulnerabilities eliminated |
| Recovery | Service restoration, validation | Business units, IT | Normal operations resumed |
Business Continuity and Disaster Recovery
ICT cyber security intersects with business continuity planning wherever incidents could disrupt operations. Organisations require documented procedures for maintaining critical functions during security incidents, including failover to backup systems, alternative communication channels, and manual processes where necessary.
Regular testing validates that backup systems function correctly and that recovery time objectives remain achievable. For many North West businesses, understanding the real cost of IT downtime provides compelling justification for investing in robust continuity capabilities.
Regulatory Compliance and Standards
UK organisations operate within an increasingly complex regulatory environment that mandates specific ict cyber security controls and reporting requirements. Understanding applicable regulations and implementing appropriate compliance programmes protects against legal and financial penalties whilst demonstrating due diligence to customers and partners.
Key Regulatory Requirements
The General Data Protection Regulation (GDPR) imposes strict requirements on organisations processing personal data, including security measures, breach notification, and data protection impact assessments. Beyond GDPR, sector-specific regulations govern industries including finance, healthcare, and critical national infrastructure.
Many government contracts and larger enterprise customers now require suppliers to demonstrate baseline security through schemes such as Cyber Essentials, which has become a condition of contract for many North West organisations.
International Standards and Frameworks
Several internationally recognised standards provide structured approaches to ict cyber security management:
- ISO/IEC 27001 defines requirements for information security management systems
- NIST Cybersecurity Framework offers risk-based guidance across five core functions
- CIS Controls provide prioritised security actions for organisations at various maturity levels
- Common Criteria establishes standards for security requirements definition
Adopting these frameworks demonstrates commitment to security best practices whilst providing structured roadmaps for continuous improvement.
Emerging Technologies and Future Challenges
The ict cyber security landscape continues evolving as new technologies introduce both opportunities and risks. Organisations must monitor emerging trends to ensure their security programmes remain effective against future threats.
Artificial Intelligence and Machine Learning
AI and machine learning technologies offer powerful capabilities for threat detection, anomaly identification, and automated response. However, these same technologies enable sophisticated attacks, including AI-generated phishing content and automated vulnerability discovery. Understanding both offensive and defensive applications of AI becomes increasingly important for ict cyber security professionals.
Internet of Things and Operational Technology
The proliferation of connected devices extends the attack surface significantly, particularly in manufacturing environments where operational technology converges with traditional IT systems. Many IoT devices lack robust security features, creating vulnerable entry points that require network segmentation and specialised monitoring.
Zero Trust Architecture
Traditional perimeter-based security models prove inadequate for organisations with cloud services, remote workers, and partner connections. Zero trust architectures eliminate implicit trust, requiring continuous verification of all users and devices regardless of location. This approach aligns well with modern ict cyber security requirements but demands significant architectural changes for many organisations.
Selecting and Working with Security Partners
Few organisations possess the internal expertise to address all ict cyber security requirements independently. Partnering with experienced managed service providers extends capabilities whilst providing access to specialist knowledge and 24/7 monitoring capabilities.
Evaluating Managed Security Service Providers
When choosing IT support partners, organisations should evaluate several key factors:
- Technical expertise across relevant security domains and technologies
- Industry experience understanding sector-specific threats and compliance requirements
- Service level agreements defining response times and availability commitments
- Scalability supporting business growth without requiring provider changes
- Cultural alignment ensuring collaborative working relationships
Managed IT support for small businesses offers particular value where internal resources cannot sustain dedicated security teams.
Ethical Considerations in ICT Security
As ict cyber security practices evolve, ethical considerations become increasingly important. The Menlo Report provides valuable ethical frameworks for security research and operations, emphasising respect for persons, beneficence, and justice. These principles should inform security programme development, particularly when implementing monitoring capabilities that could impact employee privacy.
Building Organisational Resilience
Ultimately, effective ict cyber security contributes to broader organisational resilience-the capacity to withstand disruptions, adapt to changing conditions, and recover from adverse events. Security investments should align with business objectives, supporting growth and innovation rather than constraining it.
Organisations that view security as an enabler rather than an obstacle create competitive advantages, winning customer trust and accessing opportunities unavailable to less-secure competitors. This perspective transforms ict cyber security from a cost centre into a strategic business function deserving executive attention and appropriate investment.
Building resilience requires ongoing commitment to improvement, learning from incidents, adopting new capabilities as technologies evolve, and maintaining vigilance against emerging threats. The Information Technology Industry Council emphasises that cyber security resilience depends on collaboration across organisations, sectors, and national boundaries.
Protecting your organisation's information and communications technology infrastructure demands expertise, vigilance, and comprehensive security programmes that evolve alongside emerging threats. By implementing robust ict cyber security frameworks, investing in staff awareness, and maintaining strong incident response capabilities, UK businesses can operate confidently in an increasingly digital economy. Blowfish Technology provides comprehensive managed IT and cyber security services designed specifically for North West businesses, offering the expertise and proactive support needed to keep your organisation secure and operational.

The Blowfish Technology team. Managed IT, cloud services, software development and connectivity for North West businesses since 1999.