
The convergence of information technology and operational technology has fundamentally transformed how businesses manage their critical infrastructure. Network OT represents the backbone of industrial operations, controlling everything from manufacturing lines to building management systems. As organisations increasingly connect their operational environments to broader IT networks, understanding the unique characteristics and security requirements of network OT becomes essential for maintaining both productivity and safety.
Understanding Network OT Architecture
Network OT refers to the hardware and software systems that monitor and control physical devices, processes, and events within industrial environments. Unlike traditional IT networks designed for data processing and communication, operational technology networks prioritise real-time control and deterministic behaviour. These networks must respond to physical events within milliseconds, making reliability and availability paramount concerns.
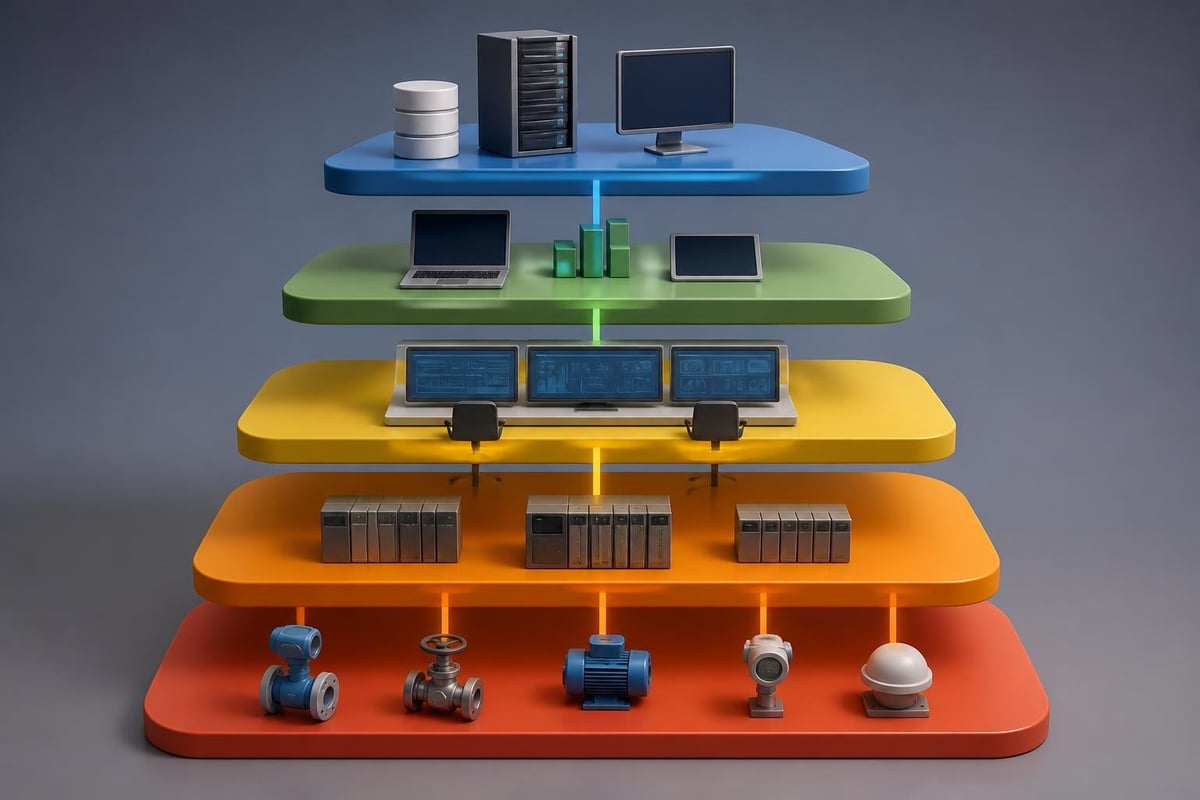
The architecture of a network OT environment typically follows a hierarchical structure known as the Purdue Model. This framework divides operations into distinct levels, from basic process control at the bottom to enterprise planning systems at the top. Each level serves specific functions and requires different security considerations.
Key Components of Network OT Infrastructure
Industrial control systems form the core of any network OT deployment. These systems include:
- Programmable Logic Controllers (PLCs) that execute control algorithms
- Supervisory Control and Data Acquisition (SCADA) systems for monitoring
- Distributed Control Systems (DCS) managing complex processes
- Human-Machine Interfaces (HMI) providing operator visibility
- Remote Terminal Units (RTUs) collecting field data
Safety Instrumented Systems (SIS) represent another critical component, designed to prevent dangerous conditions and protect personnel. These systems operate independently from primary control systems, ensuring fail-safe operations even during network disruptions.
The communication protocols used in network OT environments differ significantly from standard IT networks. Modbus, DNP3, and OPC-UA facilitate device communication, whilst specialised OT communication networks ensure efficient data flow between controllers and sensors.
Network OT vs IT Networks: Critical Differences
The fundamental distinctions between network OT and IT systems extend beyond their primary functions. These differences influence everything from design principles to security strategies, requiring organisations to adopt tailored approaches for each environment.
Availability requirements represent the most significant divergence. Whilst IT systems typically tolerate scheduled maintenance windows, network OT environments often demand continuous operation. Manufacturing facilities cannot afford unplanned downtime, as production stops can cost thousands of pounds per minute.
| Characteristic | Network OT | IT Networks |
|---|---|---|
| Priority | Availability, Safety | Confidentiality, Integrity |
| Lifespan | 15-20 years | 3-5 years |
| Change Management | Highly restricted | Regular updates |
| Response Time | Milliseconds | Seconds to minutes |
| Protocols | Modbus, DNP3, OPC | TCP/IP, HTTP, SMTP |
Understanding these operational technology versus information technology differences helps organisations develop appropriate management strategies. Network OT systems frequently run legacy operating systems that cannot be easily patched or upgraded without extensive testing and validation.
The communication patterns within network OT environments follow predictable, deterministic paths. Control loops repeat at fixed intervals, and deviations from expected behaviour often indicate serious problems. This predictability enables sophisticated monitoring approaches but also means that disruptions have immediate physical consequences.
Security Implications for Network OT
Traditional IT security approaches often prove inadequate for network OT protection. Installing antivirus software on industrial controllers might introduce latency that disrupts critical control loops. Similarly, automatic security updates could inadvertently break carefully tuned control algorithms.
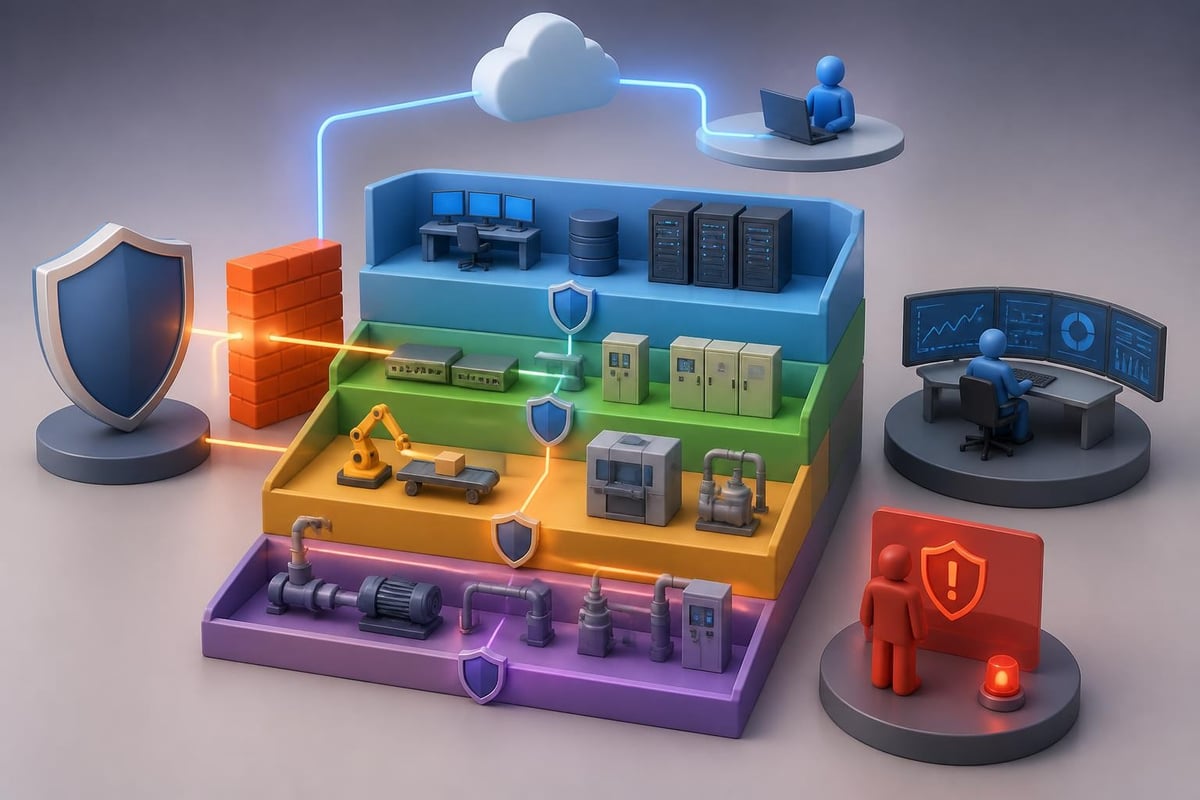
Defence in depth strategies specifically designed for network OT provide more effective protection. These approaches layer multiple security controls throughout the infrastructure, ensuring that breaches at one level don't compromise the entire system.
Network segmentation stands as perhaps the most crucial security measure. By separating IT and OT networks, organisations can optimise each environment for its specific requirements whilst limiting potential attack vectors. Firewalls, data diodes, and demilitarised zones (DMZs) create controlled pathways for necessary communication whilst blocking unauthorised access.
Designing Resilient Network OT Infrastructure
Proper OT network design requires intentional engineering that accounts for industrial conditions and operational requirements. Unlike office IT networks, network OT infrastructure must withstand extreme temperatures, electromagnetic interference, and vibration whilst maintaining deterministic performance.
Fault tolerance emerges as a primary design consideration. Redundant network paths, duplicated controllers, and failover mechanisms ensure that single component failures don't halt production. Ring topologies, for instance, provide automatic path switching when network segments fail.
Industrial-Grade Network Components
Standard commercial networking equipment rarely meets network OT requirements. Industrial switches and routers incorporate features specifically designed for harsh environments:
- Extended temperature ratings supporting operation from -40°C to 75°C
- Ruggedised enclosures protecting against dust, moisture, and vibration
- Deterministic switching ensuring predictable packet delivery times
- Power over Ethernet (PoE) simplifying device deployment
- Support for industrial protocols including time-sensitive networking
Timing and synchronisation play critical roles in many network OT applications. Precision Time Protocol (PTP) and Network Time Protocol (NTP) ensure that distributed devices maintain coordinated actions, essential for applications like motion control and protection relaying.
The physical layout of network OT cabling requires careful planning. Industrial environments generate significant electrical noise that can corrupt network signals. Proper cable routing, shielding selection, and grounding practices prevent communication errors and ensure reliable operation.
Businesses investing in managed IT services benefit from expert guidance in designing network OT infrastructure that balances performance, security, and reliability requirements specific to their operational needs.
Network OT Monitoring and Threat Detection
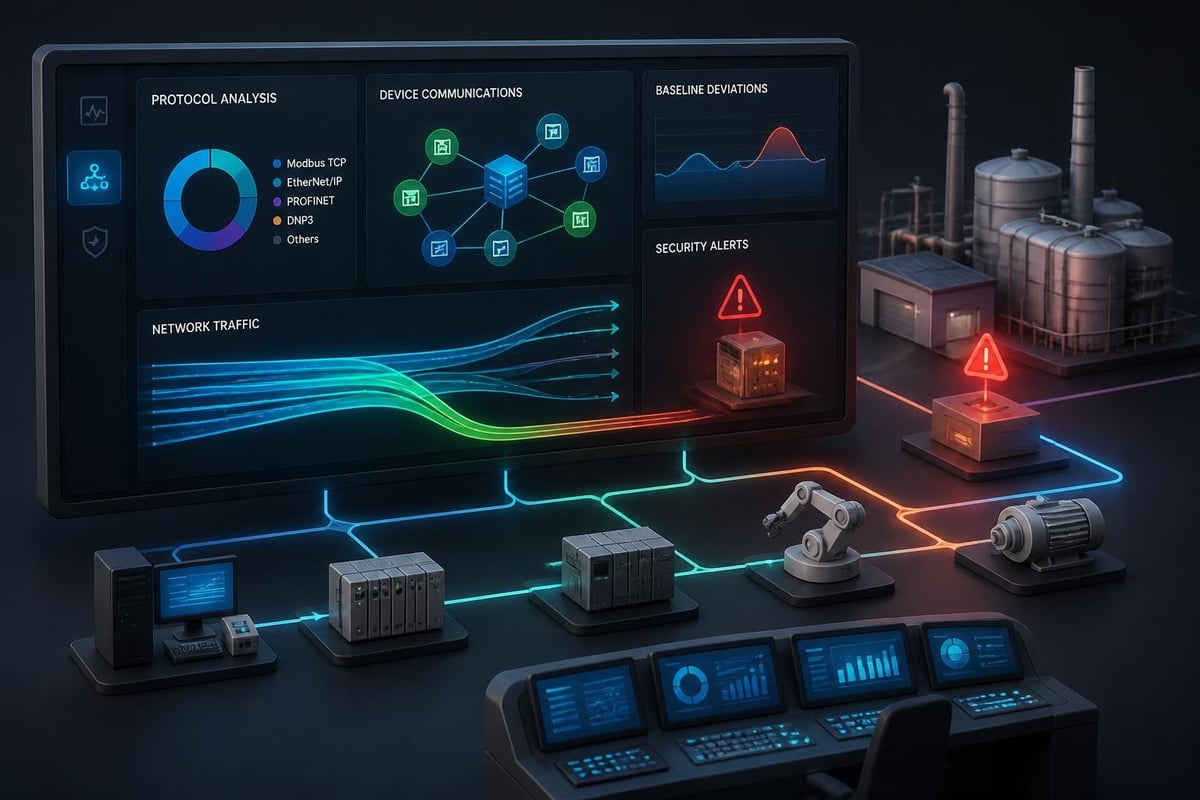
OT network monitoring serves dual purposes: ensuring operational efficiency and detecting security threats. Unlike IT network monitoring that focuses primarily on performance metrics, network OT monitoring must consider both digital and physical indicators.
Baseline behaviour establishment forms the foundation of effective monitoring. Network OT environments typically exhibit highly repetitive patterns, making anomaly detection particularly effective. When a PLC suddenly communicates with an unexpected device or traffic volumes deviate from normal ranges, these anomalies warrant immediate investigation.
Deep packet inspection tools specifically designed for network OT protocols provide visibility into industrial communications. These solutions decode Modbus, DNP3, and proprietary protocols, revealing not just that devices are communicating but precisely what commands and data they're exchanging.
Implementing Comprehensive Monitoring Strategies
Modern OT network monitoring approaches combine passive observation with active assessment:
- Network taps and span ports capture traffic without introducing latency
- Asset discovery tools maintain accurate inventories of connected devices
- Protocol analysers verify communication integrity and compliance
- Intrusion detection systems identify malicious activity patterns
- Log aggregation platforms correlate events across multiple systems
Integration between network OT monitoring and IT security operations centres creates unified visibility across converged environments. Security teams gain comprehensive awareness of threats targeting both networks, enabling coordinated response to sophisticated attacks.
The challenge of monitoring without disrupting operations requires careful tool selection and deployment planning. Network OT monitoring solutions must operate in passive modes, never injecting traffic that could interfere with control processes. Similarly, managed endpoint detection and response capabilities adapted for industrial environments provide protection without compromising performance.
Cybersecurity Challenges in Network OT Environments
The risks associated with operational technology systems have escalated dramatically as network OT environments connect to enterprise networks and cloud services. Cyber attacks targeting industrial infrastructure can cause physical damage, environmental harm, and threaten human safety, distinguishing them from typical IT breaches.
Legacy equipment poses particular challenges for network OT security. Many industrial controllers were designed decades ago when air-gapped networks provided sufficient isolation. These devices lack basic security features like authentication, encryption, and logging that modern IT systems take for granted.
Common Network OT Vulnerabilities
Understanding the attack surface helps organisations prioritise security investments. Network OT vulnerabilities typically fall into several categories:
Unpatched systems represent perhaps the most prevalent weakness. Industrial equipment often runs outdated operating systems and applications because updates risk disrupting finely tuned processes. Vendors may no longer support older platforms, leaving known vulnerabilities permanently exposed.
Weak authentication mechanisms provide attackers easy access to network OT systems. Default passwords, hardcoded credentials, and lack of multi-factor authentication enable unauthorised users to assume control of critical systems. Once inside, attackers can manipulate processes, steal intellectual property, or plant persistent backdoors.
| Threat Category | Network OT Impact | Mitigation Priority |
|---|---|---|
| Ransomware | Production shutdown | Critical |
| Supply chain attacks | Compromised firmware | High |
| Insider threats | Sabotage, data theft | High |
| Advanced persistent threats | Long-term espionage | Medium |
| Misconfiguration | Unintended exposure | Medium |
Network visibility gaps prevent security teams from detecting threats within network OT environments. Without comprehensive monitoring, attackers can operate undetected for months, studying systems and preparing devastating attacks.
The convergence of network OT and IT systems, whilst enabling beneficial capabilities like remote monitoring and predictive maintenance, also creates pathways for threats to migrate between networks. A phishing attack targeting office workers can ultimately reach production systems if proper segmentation isn't maintained.
Securing Network OT: Best Practices for 2026
Protecting network OT infrastructure requires a comprehensive strategy addressing technology, processes, and people. As cybersecurity challenges in OT networks continue evolving, organisations must adopt proactive approaches that anticipate emerging threats.
Zero Trust architecture adapted for network OT provides robust security without compromising operational requirements. Rather than trusting devices based on network location, Zero Trust verifies every access request based on device identity, user credentials, and contextual factors.
Network micro-segmentation divides network OT environments into small, isolated zones with strictly controlled communication paths. This approach limits lateral movement, ensuring that breaches remain contained within minimal scope. Implementing micro-segmentation requires thorough understanding of legitimate communication patterns to avoid disrupting operations.
Essential Security Controls
Organisations should implement layered defences specifically designed for network OT protection:
- Network access control restricting connections to authorised devices
- Application whitelisting preventing unauthorised code execution
- Secure remote access through encrypted VPN connections
- Regular vulnerability assessments identifying security weaknesses
- Incident response planning preparing for potential breaches
Patch management programmes tailored for network OT environments balance security needs with operational stability. Rather than automatic updates, these programmes involve extensive testing in isolated environments, scheduled implementation during planned maintenance windows, and comprehensive rollback procedures.
Achieving recognised security standards like Cyber Essentials Plus certification demonstrates commitment to protecting both IT and network OT infrastructure. These frameworks provide structured approaches to implementing fundamental security controls.
Network OT and Business Continuity
The relationship between network OT and business continuity extends beyond traditional disaster recovery planning. When industrial control systems fail, the consequences include production losses, safety incidents, environmental releases, and regulatory penalties. Organisations must ensure network OT resilience through comprehensive planning and robust backup strategies.
Redundancy at every level protects against single points of failure. Duplicate controllers, redundant network paths, and failover power supplies maintain operations even when individual components fail. Hot standby systems can assume control within milliseconds, preventing process upsets that might require hours to recover.
Regular testing validates that backup systems function correctly when needed. Many organisations discover their redundant systems have failed only during actual emergencies, when it's too late to address problems. Scheduled failover tests ensure all components remain operational and personnel understand recovery procedures.
Backup and Recovery Considerations
Network OT backup requirements differ significantly from IT data backup. Beyond configuration files and programs, organisations must preserve:
- Control logic and ladder diagrams defining process behaviour
- HMI screens and graphics providing operator interfaces
- Historical process data supporting trend analysis and compliance
- Network configurations enabling rapid infrastructure rebuilding
- Calibration data maintaining measurement accuracy
Implementing business backup solutions that account for both IT and network OT requirements ensures comprehensive protection. Version control systems track configuration changes, enabling recovery to known-good states when updates cause problems.
Air-gapped backups stored offline protect against ransomware that targets connected backup systems. Maintaining copies at geographically separate locations provides protection against site-wide disasters like fires, floods, or severe weather events.
Managing Network OT in Hybrid Environments
Modern businesses increasingly operate hybrid environments where network OT, traditional IT systems, and cloud services interconnect. Managing these complex ecosystems requires balancing the competing demands of operational efficiency, security, and innovation.
Cloud connectivity enables powerful capabilities like predictive maintenance, remote expert support, and advanced analytics. However, exposing network OT data to cloud platforms introduces risks that require careful mitigation. Data diodes, one-way communication gateways, allow process information to flow to cloud analytics platforms whilst preventing potentially malicious commands from reaching production systems.
Edge computing architectures process network OT data locally before transmitting summarised information to cloud platforms. This approach reduces bandwidth requirements, minimises latency, and limits exposure of sensitive operational details. Edge devices also continue functioning during internet outages, maintaining local control capabilities.
Integration with enterprise systems provides visibility across the entire organisation. When network OT data flows into business intelligence platforms, executives gain real-time insights into production efficiency, quality metrics, and resource utilisation. Secure integration points, typically located in DMZ networks, mediate these connections whilst maintaining appropriate separation.
The expertise required to manage converged IT/OT environments often exceeds what individual organisations can maintain internally. Partnering with specialists who understand both domains ensures that network OT systems receive appropriate care whilst benefiting from modern IT capabilities.
Compliance and Network OT Governance
Regulatory requirements increasingly address network OT security as governments recognise the critical importance of industrial infrastructure. Organisations operating in sectors like energy, water, manufacturing, and transportation face growing compliance obligations specific to operational technology protection.
Industry-specific standards provide frameworks for securing network OT environments. IEC 62443 addresses industrial automation and control systems security, offering detailed guidance for system design, implementation, and maintenance. NERC CIP protects bulk electric systems in North America, whilst NIS Directive governs critical infrastructure across Europe.
Documentation requirements extend beyond traditional IT systems. Network OT compliance programmes must maintain:
- Comprehensive asset inventories including industrial controllers and field devices
- Network diagrams showing all connections and communication paths
- Risk assessments identifying threats and vulnerabilities
- Security policies specifically addressing operational technology
- Evidence of security control implementation and effectiveness
Change management processes help organisations maintain compliance whilst accommodating necessary modifications. Every network OT change should undergo formal review, testing, and approval before implementation. Documented procedures ensure changes don't inadvertently violate security requirements or introduce new vulnerabilities.
Regular audits verify compliance and identify improvement opportunities. Both internal assessments and third-party evaluations provide valuable perspectives on security posture. Addressing audit findings promptly demonstrates commitment to maintaining secure network OT environments.
Protecting network OT infrastructure represents an essential priority for organisations operating industrial systems in 2026. By implementing robust security controls, comprehensive monitoring, and proper network segmentation, businesses can maintain operational efficiency whilst defending against evolving cyber threats. Blowfish Technology delivers expert managed IT and cybersecurity services specifically designed to protect both traditional IT networks and operational technology environments across the North West and throughout the UK, ensuring your critical infrastructure remains secure, compliant, and resilient.

The Blowfish Technology team. Managed IT, cloud services, software development and connectivity for North West businesses since 1999.