
In today's digital landscape, where cyber threats evolve daily and data breaches cost UK businesses millions annually, establishing robust cyber security policies has become a fundamental requirement rather than an optional extra. These policies serve as the blueprint for protecting your organisation's digital assets, defining clear protocols for everything from password management to incident response. For businesses across the North West and throughout the UK, understanding how to develop, implement, and maintain effective cyber security policies represents a critical step towards operational resilience and regulatory compliance.
Understanding the Foundation of Cyber Security Policies
Cyber security policies constitute the formal rules and procedures that govern how an organisation protects its information assets from unauthorised access, disclosure, modification, or destruction. These documented guidelines establish expectations for employee behaviour, define security responsibilities, and outline the technical controls necessary to safeguard sensitive data.
The value of well-crafted cyber security policies extends beyond mere compliance. They create a security-aware culture where every team member understands their role in protecting company assets. When employees know precisely what constitutes acceptable use of IT systems, how to identify phishing attempts, and whom to contact during security incidents, organisations significantly reduce their vulnerability to cyber attacks.
Core Components Every Policy Should Include
Essential elements that form the backbone of effective cyber security policies include:
- Acceptable Use Policy: Defines appropriate employee behaviour when using company technology and networks
- Data Classification Guidelines: Establishes how to categorise and handle different types of information
- Access Control Procedures: Specifies who can access what data and under which circumstances
- Incident Response Protocols: Outlines step-by-step actions following security breaches
- Change Management Standards: Controls how system modifications are requested, approved, and implemented
The NIST cybersecurity frameworks provide valuable guidance for structuring these components into a cohesive security programme that addresses identification, protection, detection, response, and recovery capabilities.
Developing Policies That Match Your Organisation's Risk Profile
Creating cyber security policies requires a thorough understanding of your specific threat landscape and business requirements. A manufacturing facility in Manchester faces different risks compared to a professional services firm in Liverpool, and their policies should reflect these distinctions.
Risk Assessment as the Starting Point
Begin by conducting a comprehensive risk assessment that identifies your most valuable assets, potential vulnerabilities, and likely threat actors. This analysis reveals where to focus policy development efforts and helps justify security investments to stakeholders.
| Risk Category | Example Threats | Policy Response |
|---|---|---|
| External Attacks | Ransomware, phishing, DDoS | Email security, firewall rules, incident response |
| Internal Threats | Data theft, policy violations | Access controls, monitoring, disciplinary procedures |
| Third-Party Risks | Vendor breaches, supply chain attacks | Vendor management, contract requirements |
| Compliance Gaps | GDPR violations, industry non-compliance | Data protection policies, audit procedures |
Understanding how to choose IT support that can assist with risk assessments ensures you have expert guidance throughout the policy development process.
Tailoring Policies to Business Operations
Generic, one-size-fits-all cyber security policies rarely deliver optimal protection. Your policies must align with operational workflows whilst maintaining security rigour. For instance, a business relying heavily on remote workers needs comprehensive policies around VPN usage, home network security, and secure collaboration tools.
Consider how different departments interact with technology. Your finance team requires strict data handling procedures for sensitive financial information, whilst your marketing department needs guidelines for managing customer data in CRM systems and email platforms. The comprehensive approach to managed IT support helps ensure policies remain practical and enforceable across all business functions.
Implementation Strategies That Drive Adoption
Even brilliantly written cyber security policies achieve nothing if employees don't understand or follow them. Successful implementation requires strategic communication, comprehensive training, and ongoing reinforcement.
Launching Your Policy Framework
Implementation success factors include:
- Executive Sponsorship: Secure visible support from senior leadership to demonstrate organisational commitment
- Clear Communication: Explain why policies matter and how they protect both the company and employees
- Accessible Documentation: Make policies easy to find, read, and reference through your intranet or document management system
- Phased Rollout: Introduce policies gradually rather than overwhelming staff with numerous requirements simultaneously
- Feedback Mechanisms: Create channels for employees to ask questions and suggest improvements
The five best practices for IT security policies emphasise regular updates and alignment with organisational needs, ensuring policies evolve alongside business changes.
Training and Awareness Programmes
Policy documentation alone won't change behaviour. Invest in regular training that helps employees understand security concepts, recognise threats, and respond appropriately to incidents. Given that 90% of cyber security attacks start with a simple email, phishing awareness training should feature prominently in your programme.
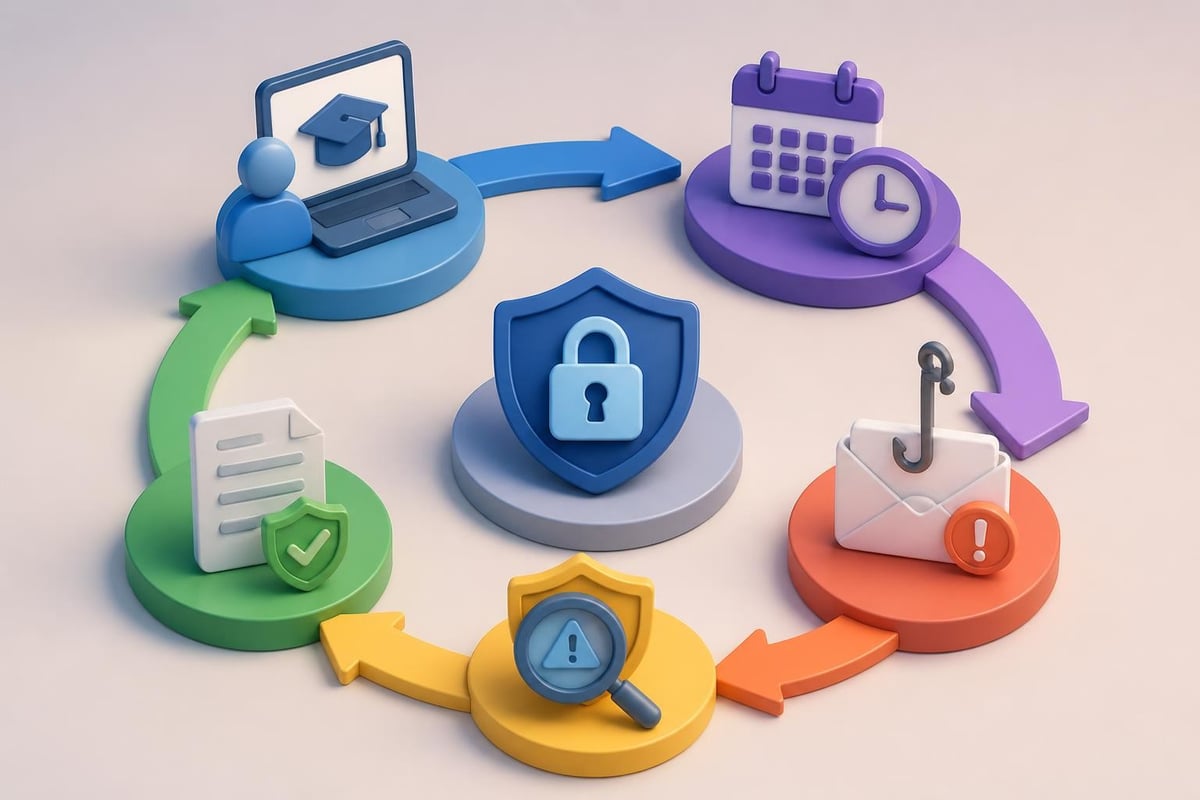
Quarterly awareness sessions, monthly security newsletters, and simulated phishing exercises keep security at the forefront of employee consciousness. Track participation rates and test scores to identify departments requiring additional support.
Essential Policy Categories for Modern Businesses
Comprehensive cyber security policies span multiple domains, each addressing specific aspects of your security posture. Prioritising these categories ensures balanced protection across your technology environment.
Network and Infrastructure Security
Your network represents the foundation supporting all business operations. Policies governing network security should address firewall configurations, network segmentation, wireless access controls, and remote access procedures. For businesses considering switching from broadband to leased lines, network security policies must evolve to reflect the enhanced connectivity and associated security requirements.
Cloud Security and Data Protection
As organisations migrate workloads to cloud platforms, cyber security policies must extend beyond traditional perimeter defences. Define clear guidelines for cloud service selection, data storage locations, encryption requirements, and access management. Your cloud migration strategy should incorporate security considerations from the outset, ensuring policies align with architectural decisions.
| Policy Area | Key Requirements | Review Frequency |
|---|---|---|
| Password Management | Complexity, rotation, multi-factor authentication | Quarterly |
| Mobile Device Security | Encryption, remote wipe, approved applications | Bi-annually |
| Email Security | Anti-spam, attachment scanning, phishing protocols | Quarterly |
| Backup and Recovery | Frequency, retention, testing schedules | Monthly |
The importance of cybersecurity policies extends to protecting business continuity, making disaster recovery and backup policies particularly critical components of your security framework.
Third-Party and Vendor Management
Cyber security policies must address the risks introduced through third-party relationships. Establish requirements for vendor security assessments, contractual security obligations, and ongoing monitoring of supplier security posture. This becomes especially important when selecting managed service providers who require access to your systems and data.
Compliance and Regulatory Considerations
Cyber security policies serve a dual purpose: protecting assets whilst demonstrating compliance with legal and industry requirements. Understanding relevant regulations ensures your policies meet mandatory standards.
GDPR and Data Protection
UK businesses handling personal data must align cyber security policies with GDPR requirements. This includes policies for data minimisation, lawful processing, breach notification, and individual rights. Document how your organisation implements privacy by design principles and maintains records of processing activities.
Industry-Specific Standards
Different sectors face unique regulatory requirements. Healthcare organisations must address NHS Digital standards, financial services firms comply with FCA requirements, and government contractors increasingly find Cyber Essentials becoming a condition of contract. Ensure your cyber security policies explicitly address applicable industry frameworks.
The ten cybersecurity best practices for businesses include implementing multiple layers of defence and continuous vulnerability scanning, both essential elements for maintaining compliance across various regulatory regimes.
Incident Response and Business Continuity
No security framework remains impenetrable. Effective cyber security policies acknowledge this reality by establishing clear incident response procedures that minimise damage and accelerate recovery.
Building an Incident Response Plan
A comprehensive incident response plan forms a critical component of your cyber security policies. This document should define:
- Detection and Analysis: How security incidents are identified and assessed
- Containment Strategies: Immediate actions to prevent incident escalation
- Eradication Procedures: Steps to remove threats from your environment
- Recovery Processes: Methods for restoring normal operations
- Post-Incident Review: Lessons learned and policy improvements
Understanding what a good cyber security incident response plan looks like helps organisations prepare comprehensive procedures that address clear roles, regular updates, and communication strategies.
Maintaining Business Continuity
Cyber security policies should integrate with broader business continuity planning. Define recovery time objectives (RTO) and recovery point objectives (RPO) for critical systems, ensuring backup policies support these targets. Given that IT downtime costs North West businesses significant revenue, policies addressing how to reduce IT downtime become essential business protection measures.
Policy Maintenance and Continuous Improvement
Cyber security policies require regular review and updates to remain effective against evolving threats. Static policies quickly become obsolete as technology changes, new vulnerabilities emerge, and business operations adapt.
Establishing Review Cycles
Maintain policy relevance through:
- Annual comprehensive reviews: Assess all policies against current threat landscape and business requirements
- Quarterly targeted updates: Revise specific policies responding to security incidents or technology changes
- Event-triggered modifications: Update policies following significant business changes, mergers, or major security incidents
- Regulatory monitoring: Track legislative changes requiring policy adjustments
The types of cybersecurity policies and best practices highlight the significance of tailoring policies to organisational structure and risk profile, emphasising ongoing adaptation rather than set-and-forget approaches.
Measuring Policy Effectiveness
Track metrics demonstrating whether cyber security policies achieve intended outcomes. Monitor security incident frequency, employee policy compliance rates, audit findings, and time-to-respond metrics. Regular testing through penetration tests, tabletop exercises, and policy audits reveals gaps requiring attention.
Framework Selection and Standards Alignment
Aligning cyber security policies with recognised frameworks provides structure and demonstrates best practice adherence. Several frameworks offer valuable guidance for policy development.
Popular Cybersecurity Frameworks
| Framework | Best Suited For | Key Benefits |
|---|---|---|
| NIST Cybersecurity Framework | Organisations of all sizes | Flexible, comprehensive, risk-based approach |
| ISO/IEC 27001 | Businesses seeking certification | International recognition, systematic methodology |
| CIS Controls | Small to medium businesses | Prioritised, actionable security measures |
| COBIT | IT governance focus | Business alignment, regulatory compliance support |
The seven key cybersecurity frameworks provide detailed structures and applications for managing cyber risks across diverse organisational contexts.
Benefits of Framework Adoption
Adopting established frameworks accelerates policy development by providing tested templates and comprehensive control catalogues. Frameworks also facilitate communication with stakeholders, customers, and regulators who recognise standard approaches to cyber security governance.
Overcoming Common Implementation Challenges
Many organisations struggle to translate cyber security policies from documentation into effective practice. Recognising common obstacles helps you develop strategies to overcome them.
Resource Constraints
Small and medium-sized businesses often lack dedicated security personnel to develop and maintain cyber security policies. Challenges small businesses face in implementing cybersecurity strategies include bridging the gap between planning and execution. Partnering with experienced managed service providers addresses this challenge by accessing expertise without building internal security teams.
Balancing Security with Productivity
Overly restrictive cyber security policies frustrate employees and hinder productivity, often leading to workarounds that undermine security objectives. Involve end-users in policy development to ensure requirements remain practical whilst maintaining appropriate protection levels. Policies should enable secure work rather than merely prohibit risky behaviour.
Achieving Consistent Enforcement
Inconsistent policy enforcement erodes credibility and creates security vulnerabilities. Ensure all staff, regardless of seniority, adhere to cyber security policies. Implement technical controls that automate enforcement where possible, removing subjective decision-making and reducing the burden on employees.
Technology Supporting Policy Enforcement
Technical controls complement cyber security policies by automating enforcement and reducing reliance on human compliance. Strategic technology investments strengthen your security posture whilst simplifying policy adherence.
Essential Security Technologies
Modern security tools support policy objectives across multiple domains. Email security gateways enforce policies around attachment types and external communications. Data loss prevention systems automatically block policy violations involving sensitive information transfer. Endpoint protection platforms ensure devices meet security standards before accessing network resources.
Understanding the benefits of cloud infrastructure for business includes recognising how cloud platforms provide built-in security features supporting policy requirements, from encryption to access logging.
Monitoring and Compliance Tools
Security information and event management (SIEM) platforms centralise log collection and analysis, enabling continuous monitoring of policy compliance. These systems detect anomalous behaviour indicating policy violations or security incidents, triggering alerts that prompt investigation and response.
Effective cyber security policies form the cornerstone of organisational resilience against an ever-evolving threat landscape. By developing comprehensive policies aligned with business objectives, implementing them through strategic training programmes, and maintaining them through regular reviews, UK businesses create sustainable protection for their digital assets whilst meeting regulatory obligations. Blowfish Technology provides expert guidance on developing, implementing, and maintaining cyber security policies tailored to your specific operational requirements, backed by comprehensive managed IT and security services that transform policy frameworks into practical protection across the North West and throughout the UK.

The Blowfish Technology team. Managed IT, cloud services, software development and connectivity for North West businesses since 1999.